Mastering Conditional Payment Gateways in WooCommerce
Modern WordPress engineering requires an in-depth understanding of system architecture, filter execution pipelines, and data consistency. In this comprehensive guide, we will explore conditional payment methods with clean architectural standards, robust security practices, and scalable implementation strategies.

Core Architecture and Lifecycle Hooks
When implementing conditional payment methods in production environments, developers must ensure that hooks run at the appropriate priority level. Tapping into the correct WordPress and WooCommerce actions guarantees that dependent services, session objects, and database states are fully initialized before execution begins.
Furthermore, managing high-volume stores demands defensive programming. Always sanitize incoming payloads, validate contextual permissions, and handle null edge cases gracefully to avoid fatal exceptions during critical customer checkout or administrative workflows.
Step-by-Step Implementation
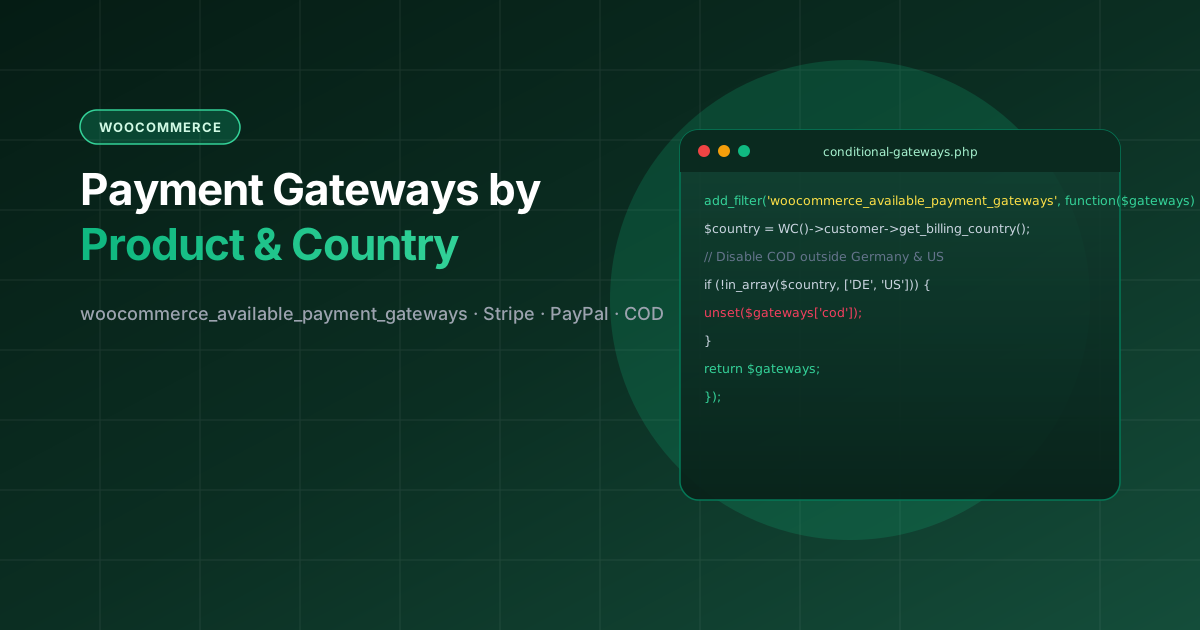
Below is the recommended, production-tested code pattern for managing conditional payment methods. This snippet follows WordPress coding standards, ensures compatibility with modern PHP 8 features, and respects database query caching best practices.
add_filter('woocommerce_available_payment_gateways', function($available_gateways) {
    if (is_admin()) {
        return $available_gateways;
    }

    $billing_country = WC()->customer ? WC()->customer->get_billing_country() : '';

    // 1. Disable Cash on Delivery outside Germany and United States
    if (!in_array($billing_country, ['DE', 'US'], true) && isset($available_gateways['cod'])) {
        unset($available_gateways['cod']);
    }

    // 2. Disable PayPal when buying high-risk digital gift cards
    foreach (WC()->cart->get_cart() as $item) {
        if (has_term('gift-cards', 'product_cat', $item['product_id'])) {
            unset($available_gateways['paypal']);
            break;
        }
    }

    return $available_gateways;
}, 100);
Key Architectural Considerations
- Execution Timing: Hook callbacks should never trigger heavy database queries unconditionally. Always verify request contexts such as
is_admin()or active query flags. - Data Sanitization: Any data extracted from request bodies or global superglobals must be thoroughly sanitized using core helpers such as
sanitize_text_field()orwp_unslash(). - Cache Invalidation: Whenever updating term taxonomies, product metadata, or options, ensure that relevant object caches and transient stores are invalidated properly.
Fraud Prevention and Regulatory Compliance
Payment gateways carry varying merchant service fees and chargeback liabilities. By restricting high-risk gateways to domestic or verified transactions, merchants protect profit margins and streamline cash flow reconciliation.
Testing and Verification
Automated integration tests with PHPUnit provide absolute confidence when refactoring or deploying changes. Always mock network responses, verify database transactions, and test boundary conditions to prevent regressions in production.
Summary and Best Practices
By adhering to these proven design patterns for conditional payment methods, your WordPress applications remain fast, secure, and easily maintainable. Regularly test your custom logic against staging environments and monitor query performance metrics to deliver exceptional user experiences.